

Aave V3.8 proposal puts callback safety ahead of new features
A proposed reentrancy guard would harden lending operations; audits and governance still precede deployment.
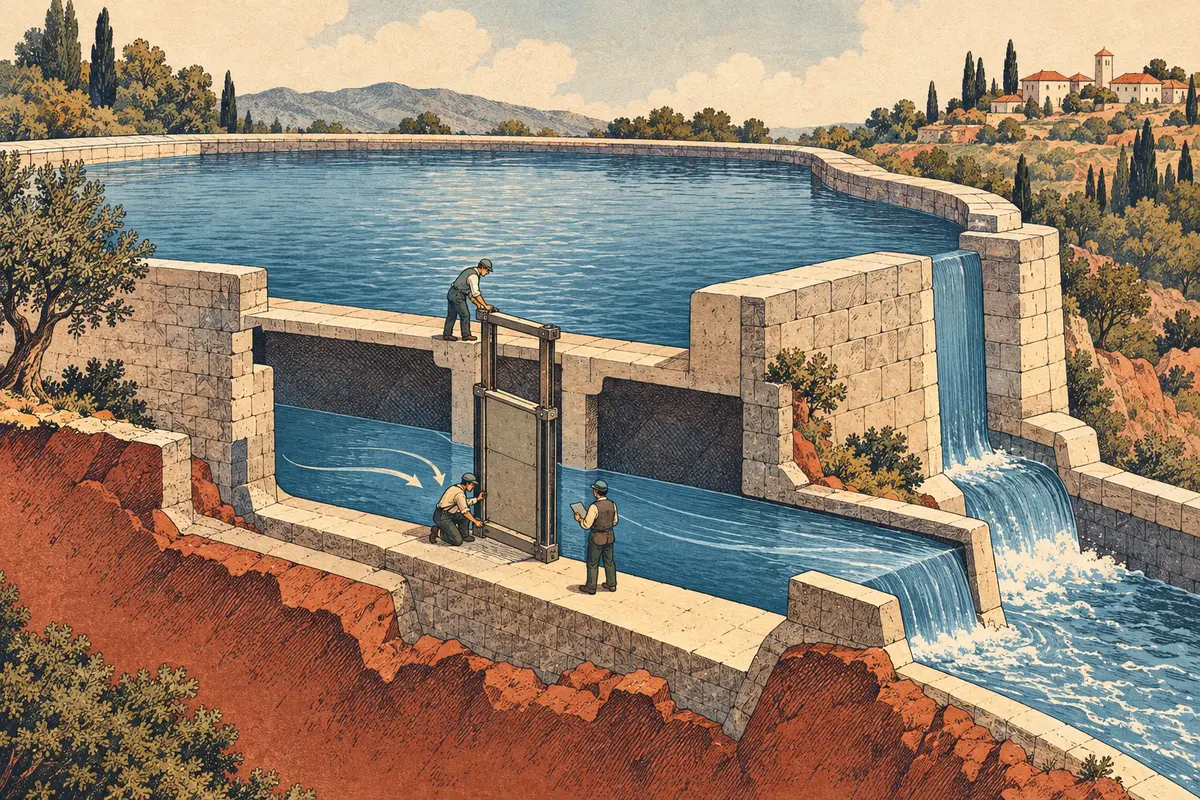
Aave Labs proposed V3.8 on October 21, adding a transient-storage guard against reentrancy during external callbacks. The governance post describes a security upgrade, with audits and subsequent voting still ahead. It does not establish a live rollout.
The practical issue is accounting consistency when execution leaves a lending pool and later returns within the same transaction. For teams integrating lending into treasury or payment products, this is a reminder that composability also creates a responsibility to understand callbacks and failure behavior.
Our reading: integration teams should map their transaction paths before an upgrade lands, including adapters, automated repayments and error recovery. A narrowly scoped change can still affect assumptions in surrounding software. A passing happy-path transaction alone says little about interrupted or repeated execution.
For Panama builders, the useful next step is preparation: identify dependencies, review the eventual audited implementation and test representative workflows against the relevant deployment. Treat the proposal as a chance to improve integration discipline, rather than a promise that lending risk has disappeared.